
Hackers Disrupt Real World from Refrigerators to Blood Banks as Cyber Threats Spread Across European Retail Businesses - Thairath English
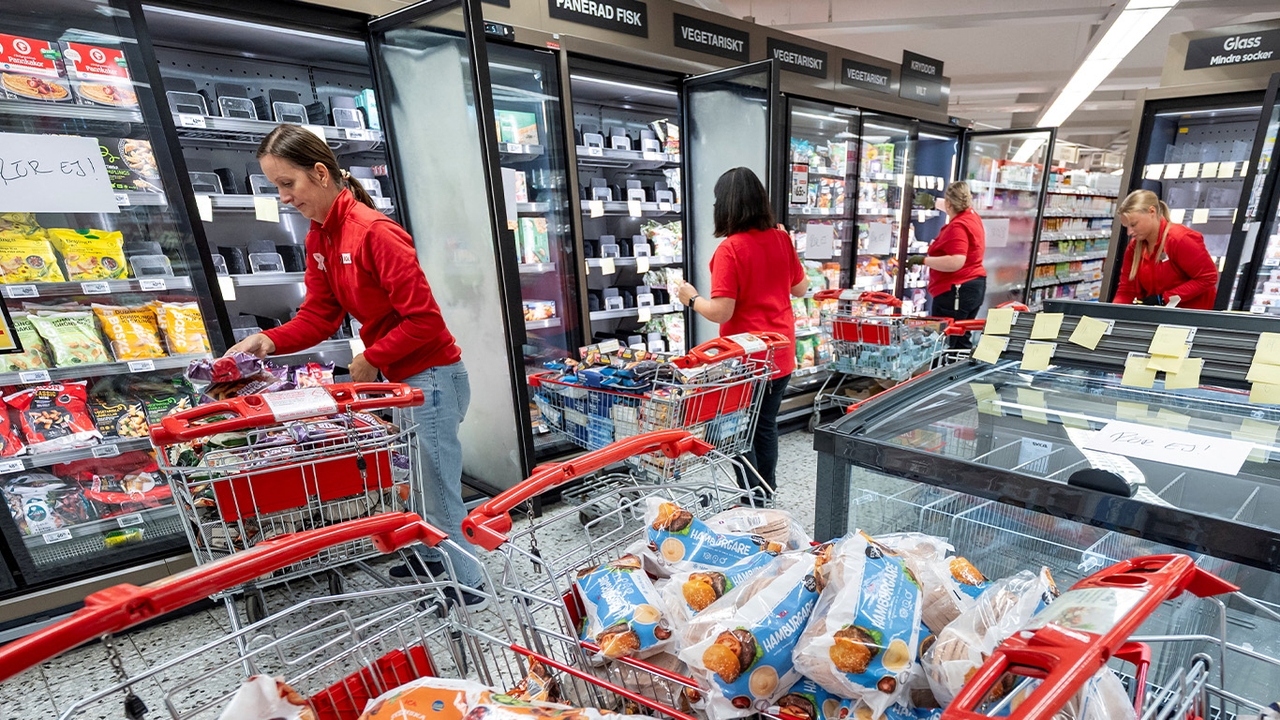
Cyber threats may no longer be as distant as once thought, as hacker attacks extend beyond data theft, ransom demands, or online system outages, increasingly targeting systems that control everyday life and economic activities—from manufacturing, transportation, retail, to public health services directly affecting people's lives.
The latest wave of cyberattacks in Europe saw hackers breach supermarket refrigeration control systems in several countries, remotely adjusting temperatures and spoiling products. Similar incidents then spread to plasma storage systems in French blood banks, highlighting that vulnerabilities in internet-connected technology can cause impacts beyond digital damage.
Meanwhile, the economic impact is becoming increasingly evident asAhold Delhaizethe major Dutch retail company estimates these incidents could reduce Q4 sales by up to 250 million euros (about 9.4 billion baht) and operating profits by as much as 100 million euros (around 3.8 billion baht).
Although the attacks targeted only parts of operating systems, these figures underscore the significant economic costs cyber threats can impose, potentially escalating to damage worth several billion baht.
The latest attacks occurred between 1-2 November 2026, following similar incidents first reported in France on 11 October, then spreading to retail stores across more than 10 European countries including Belgium, Sweden, Luxembourg, Ireland, the Netherlands, Finland, and Estonia.
Targets included not only small shops but also large supermarket and retail chains such as Carrefour, Delhaize, ICA, Coop, SuperValu, and some IKEA branches.
In Belgium, about 40 Delhaize supermarkets and retail outlets were affected, along with 15 Carrefour stores, 15 Intermarché, and 5 Spar locations. In Sweden, ICA stores numbered 23 and Coop 7, while Ireland saw 13 SuperValu outlets impacted.
Some locations reported abnormal temperature spikes inside refrigeration units, such as an ICA store in Stockholm recording temperatures as high as 50 degrees Celsius. A Belgian butcher estimated losses of about 15,000 euros (approximately 560,000 baht) due to spoiled meat.
Although many stores remained open, they had to quickly remove potentially unsafe fresh and frozen foods, inspect cooling systems, and replace some equipment to prevent recurrence. Beyond lost sales, retailers faced costs for system checks, repairs, and business disruptions.
Another concerning incident occurred on 2 November 2026, when Établissement français du sang (EFS), France’s national blood service, disclosed that temperature control systems at three plasma storage sites were cyberattacked.
Reports indicated attackers altered temperature controls and defrosting parameters, attempting to change settings from the normal -30 degrees Celsius to as high as 110 degrees Celsius. However, the 110-degree figure was an attempted setting by attackers, not the actual recorded temperature inside storage.
This system is critical for preserving plasma used in patient treatments and drug production, requiring strict temperature regulation to maintain product quality and safety.
EFS confirmed its monitoring and alarm systems quickly detected anomalies, allowing staff to manage the situation and transfer plasma to secure storage safely.In timeThe incidentresulted in no reported damage to blood products or patient impact, and blood donation and distribution continued normally.
Although plasma was unharmed, this case highlights a unique risk compared to typical business attacks; if temperature control systems for medical supplies are tampered with undetected, consequences could extend to healthcare readiness and patient safety.
What makes this incident notable is that targets were not customer databases, payment systems, or company websites, but control systems operating inside facilities.
Many commercial refrigeration systems today connect to the internet, enabling operators to remotely monitor temperature, performance, and manage equipment. While this reduces operating costs—especially for retailers with many branches—it also opens new access points for attackers if security is inadequate.
Reports from Belgium indicate attackers forced devices into Defrost Mode, causing abnormal temperature rises. Previously identified vulnerabilities included direct internet access to control systems, outdated unpatched software, and weak security settings.
In the French blood bank case, attackers did not access EFS’s main IT systems directly but targeted cooling systems operated by third-party providers.
Coolworld, the refrigeration service provider involved, acknowledged cybersecurity issues, stating the reported vulnerabilities related to technology components from other providers.
This reflects a Third-party or Supply Chain Cyberattack risk, where organizations suffer from vulnerabilities in external service providers, even without direct breaches of their own core systems. However, full technical details have not been released, so it’s unclear if all affected countries faced the same vulnerabilities or attackers.
Following these events, the European Commission and the EU cybersecurity agency ENISA jointly stated on 4 November 2026 that they are closely monitoring incidents affecting commercial refrigeration systems in several member states.
They are cooperating with Europol and national cybersecurity bodies to share threat intelligence, investigate vulnerabilities, and prevent further attacks.
So far, no perpetrators or motives have been confirmed, nor is there sufficient evidence to confirm links between incidents in different countries. Moreover, no ransom demands have been reported, raising questions whether the attacks aim not for financial gain but to cause damage or disrupt operations, though motives remain unconfirmed.
These refrigeration system attacks in Europe come amid growing concerns over cybersecurity in critical infrastructure, following incidents impacting real-world business operations at major organizations.
In September 2025, ransomware attacks on Collins Aerospace’s check-in and boarding systems disrupted services at London Heathrow, Brussels Airport, and Berlin Brandenburg airports, forcing some airlines to revert to manual check-ins and causing flight delays.
Around the same time, British automaker Jaguar Land Rover faced cyberattacks thathalted production lines, affectingoperations and supply chain businesses.
The ENISA Threat Landscape 2026 report analyzing European cyber incidents in 2025 found government agencies were the most targeted group, accounting for 32% of studied cases, followed by service businesses and transport sectors at 8% each, manufacturing at 7%, and finance and banking at 6%.
Additionally, 73% of targeted organizations were classified as essential or critical under the EU’s NIS2 legal framework, indicating cyber threats increasingly endanger services and economic activities on which citizens rely daily.
A common thread among these events is reliance on digital systems and technologies from external providers, enhancing business efficiency but enabling a single vulnerability to impact multiple organizations or countries—especially Internet of Things (IoT) and Operational Technology (OT) systems that link digital control with real-world equipment and processes, from refrigeration units and factory machinery to transport and medical devices.
The supermarket and blood bank incidents in Europe exemplify how cyberattacks can extend beyond data breaches or online outages to directly affect products, revenues, business continuity, and public safety.
The key question for businesses is not only how to prevent hackers from accessing data but also how to prepare for attacks on digital systems controlling real-world operations, as a single cyber vulnerability can cause economic damage far greater than many organizations anticipate.
https://www.thairath.co.th/money/economics/thai_economics
Follow the Facebook page Thairath Money at the link https:// www.facebook.com/ThairathMoney

